Control Generative AI
Across Every Organization
FlowGuard detects and manages sensitive data exposure, Shadow AI usage, and policy violations across ChatGPT, Copilot, Claude, and 40+ AI services.
No Input. Still Leaked.
Through MCP, AI connects straight into wikis, databases, ticketing systems, and code repositories and pulls data on its own. Prompt inspection sees none of it.
From Prompt Checks
to Action Guardrails
The control point is moving from what was typed to what the agent did. FlowGuard AI is extending the platform in exactly that direction.
40+
AI Services Monitored
13,000+
Shadow AI Database
Real-time
Detection & Blocking
5 min
Time to Deploy
Two-stage control
Who, and where to
Blocks personal accounts and unapproved tenants, leaving only the approved corporate workspace.
And what gets sent
Inside the approved tenant, sensitive data is still detected, masked or blocked, and logged.
The Problem
Uncontrolled AI Usage
Threatens Enterprise Security
The first wave of risk was what an employee typed. As AI connects into internal systems and calls tools on its own, what the AI did is becoming the new risk on top of it.
01
Sensitive Data Leakage
Employees inadvertently submit PII, source code, trade secrets, and financial data to external AI services.
02
Shadow AI Usage
Over 13,000 AI tools operate outside IT approval, with no security policy coverage or visibility.
03
Unenforceable Policies
Policies like "don't enter confidential data into AI" cannot be enforced without technical controls.
04
No Security Visibility
Security teams have no way to know which departments use which AI tools with what data.
05
New waveAgent Access to Internal Systems
Through MCP, AI connects straight into wikis, databases, ticketing systems, and code repositories. Data moves even when nobody types anything sensitive.
06
New waveNo Audit Trail for Tool Calls
Without a record of which tools an agent invoked, with what arguments, and what it changed, neither incident analysis nor regulatory response is possible.
How It Works
FlowGuard Monitors and Controls
AI Usage
Warn or block sensitive data inputs per policy, and log every event in an auditable format. The four steps below are the control flow available today.
Detect & Visualize Usage
Detect usage of 40+ AI services in real time, with visibility by department, user, and AI app.
Sensitive Data Detection
Analyze AI inputs to detect PII, source code, financial data, and medical information in real time.
Policy-Based Control
Warn or block sensitive inputs in real time. Policies apply at the organization, department, or user level.
Logging & Audit Reports
Log all detection events and enforcement results for compliance audits and security analysis.
Watch
See FlowGuard in Action
The brand film for the whole picture, the CAC + AI DLP film for how the account and the prompt get covered together.
Product Demos
Confidential Document Leak Detection
Confidential Document Leak Detection
Click to launch demo
Sensitive Data Leak Detection
Sensitive Data Leak Detection
Click to launch demo
Key Capabilities
Six Security Capabilities Available Today
Sensitive Data Detection
Detects 130+ sensitive data types — PII, source code, financial data, medical information, and trade secrets — in real time.
GenAI Input Monitoring
Monitor actual inputs to 40+ AI services including ChatGPT, Claude, Gemini, Copilot, and Cursor.
Policy-Based Control
Apply granular security policies by organization, department, or user to automate warnings, blocking, and logging.
Shadow AI Detection
Detect 13,000+ AI tools used without IT approval and enforce allow/block policies across all of them.
User & Dept Risk Analysis
Analyze risk scores and detection events by user, department, and AI app to identify high-risk behavior patterns.
Audit Logs & Reports
Comprehensive reports on AI usage, sensitive data detection, policy violations, and user behavior analytics.
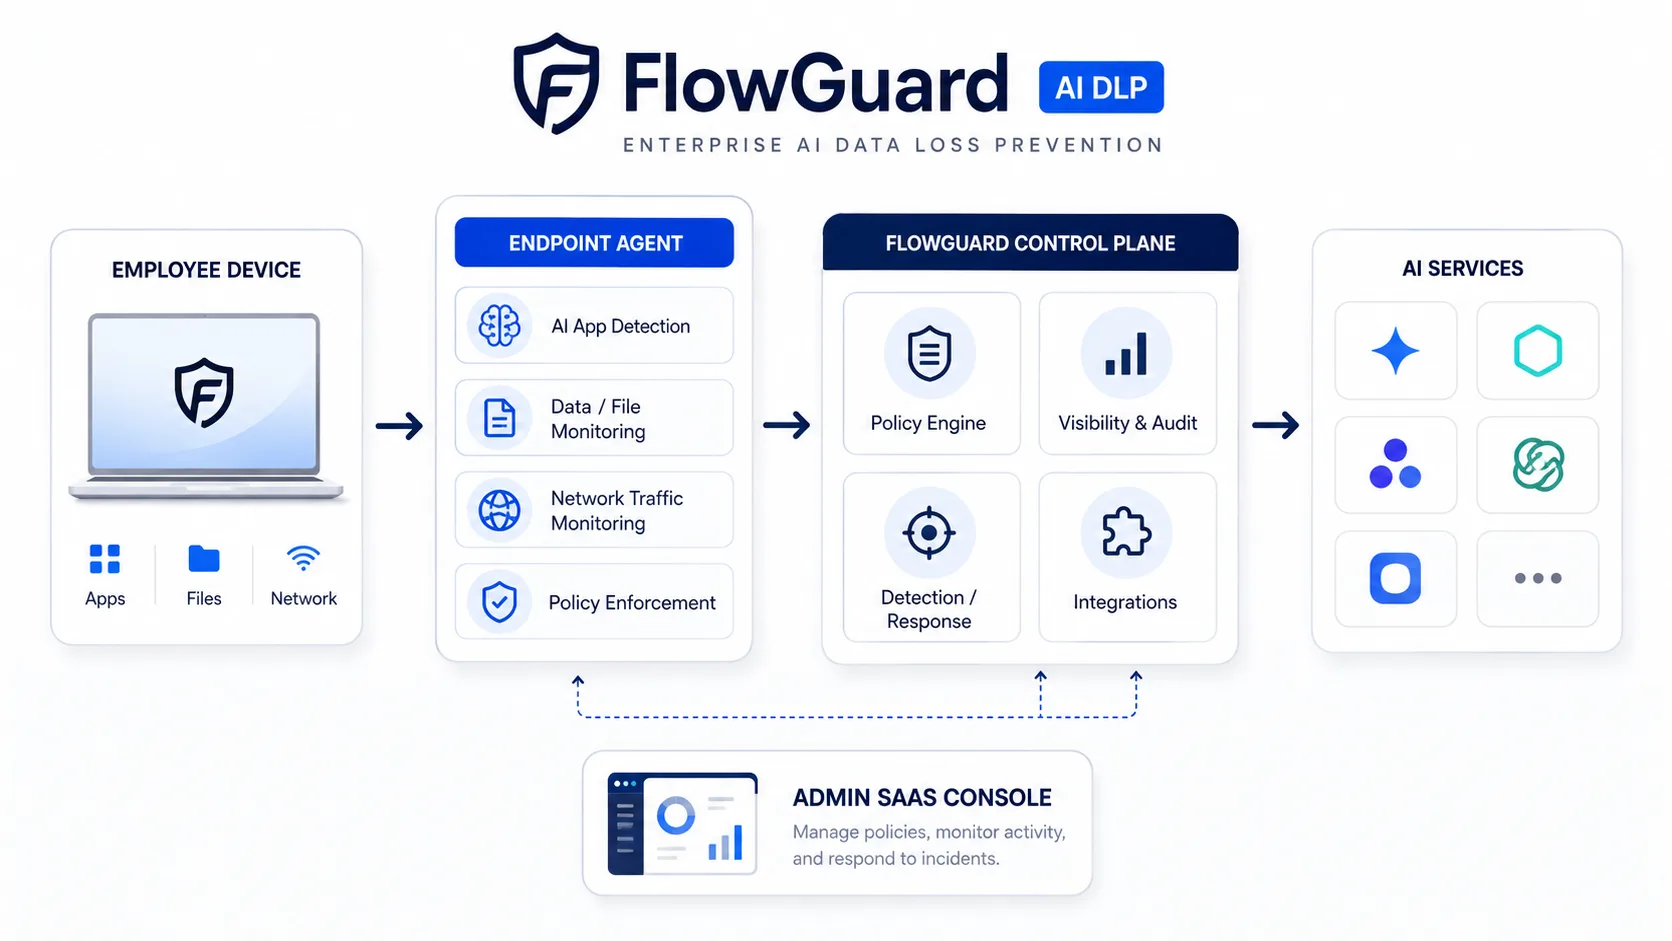
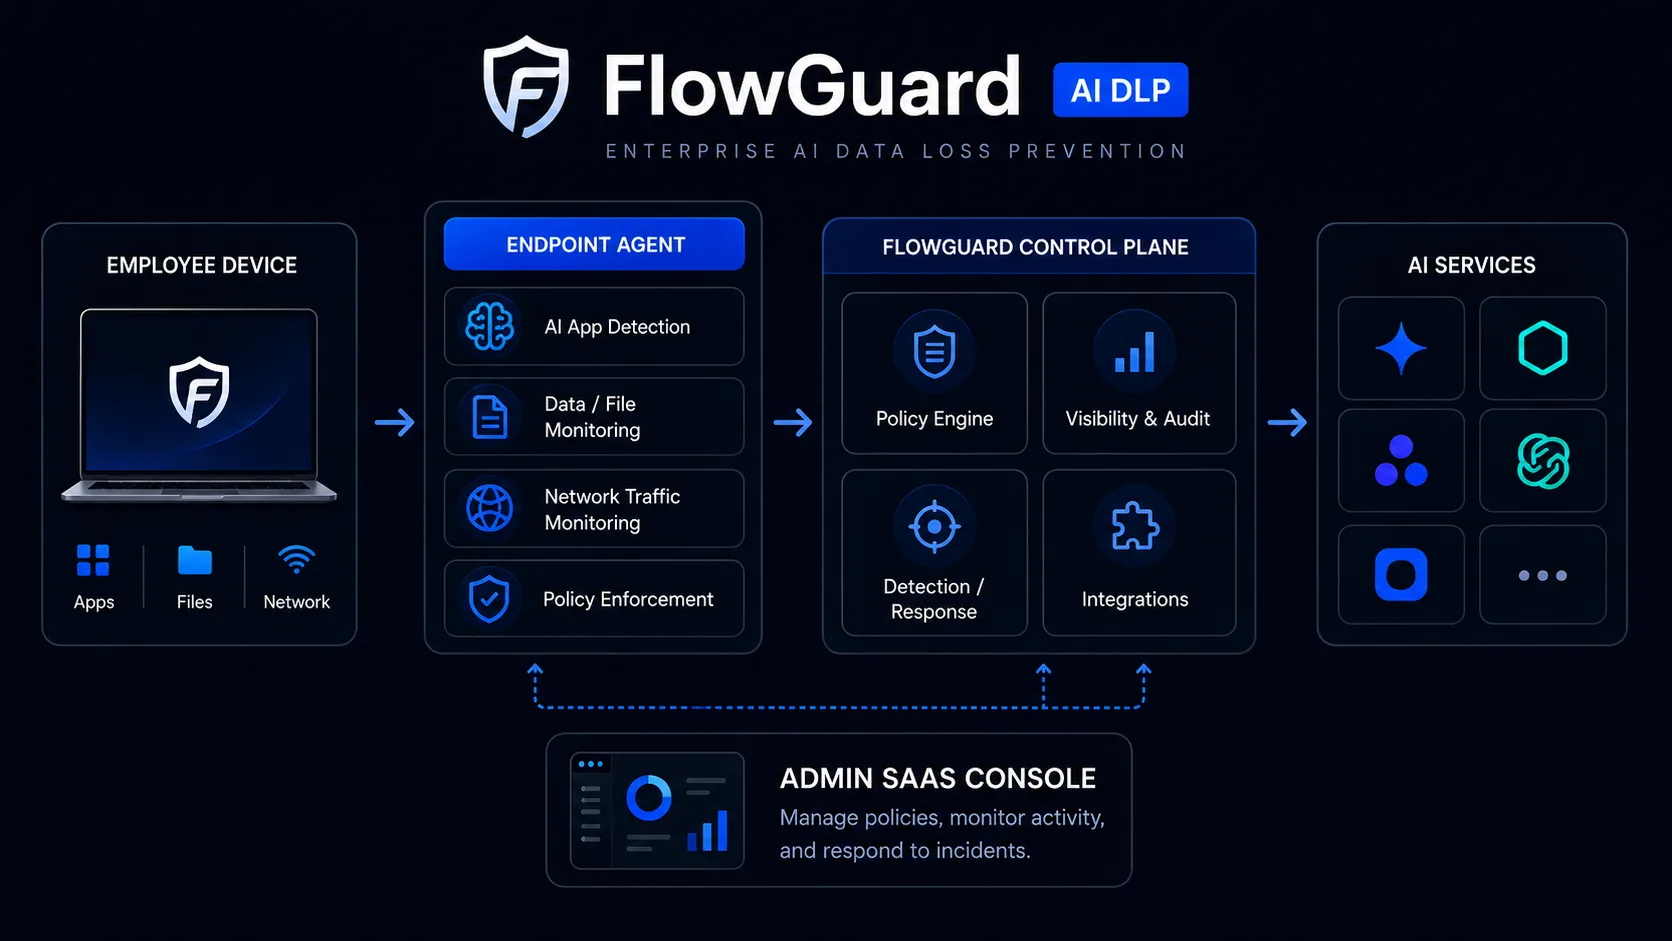
Security Architecture
Integrated Security Flow
from Endpoint to Admin Console
See where data is detected, how policy decisions are made, and where events are recorded.
Use Cases
Built for Every Organization
Handing AI More Work
Finance & Insurance
InfoSec Team- Comply with financial security regulations
- Prevent AI leakage of customer financial data
- Maintain auditable employee AI usage logs
Public Sector
Security Officer- Prevent AI leakage of government documents
- Meet mandatory audit logging requirements
- Control AI in air-gapped environments
Enterprise & Manufacturing
CISO / InfoSec- Block leakage of trade secrets and designs
- Enterprise-wide AI usage visibility
- Apply differentiated policies by department
IT & Software
Engineering / Security- Prevent code leakage via Copilot and Cursor
- Approval and control of developer AI tools
- Scope MCP integrations and agent tool access
Healthcare & Bio
Health Data Security- Prevent AI leakage of patient and clinical data
- HIPAA and healthcare law compliance
- Monitor and report clinician AI usage
Agent-Adopting Enterprises
AI Adoption Team- Detect Shadow AI and run approval workflows
- Set and enforce enterprise AI policy
- Know which internal systems agents reach, and with what scope
Where we're going
Next: MCP and AI Guardrails
Not in the product yet — these are the problems we're taking on next.
MCP Connection Visibility
Nobody has an inventory of which agents reach which internal systems, or under what scope.
Action Guardrails
There is still no way to screen a tool call against policy in the moment before it runs.
Indirect Prompt Injection
Text planted in a document or ticket the agent reads still works as an instruction.
Agent Action Audit
With no record of what was called or what changed, there is nothing to trace after an incident.
Your data is safe with us
Built with security and compliance at the core
Security Features
- End-to-end AES-256 encryption
- Role-based access control (RBAC)
- Multi-factor authentication (MFA)
- Real-time threat detection
- Automated security audits
- Data residency compliance
Protected Data Types
Personal Identifiable Information (PII)
Internal Identifiers
Authentication & Security (Critical)
Financial Information
Medical & Health (PHI)
Legal & Contract Documents
Sales & Strategy
Technology & IP
Trade Secrets
Do You Know What You've Handed AI?
In most organizations AI tools are already wired into internal systems, and security has no inventory of them. FlowGuard AI starts by building that inventory.
No credit card required • Free 14-day trial • Cancel anytime